Systematic testing for injection flaws (SQLi, command injection), broken authentication, cross-site scripting (XSS), broken access control, security misconfiguration, and insecure deserialization: the vulnerability classes responsible for the vast majority of real-world web breaches.
Web Application Security
Protecting web applications against the most common and most damaging attack vectors.
Mobile Application Security
Securing iOS and Android applications against device-level and network-level threats.
API Security
APIs are the connective tissue of modern applications: and one of the most commonly under-tested attack surfaces.
Server & Infrastructure Security
Hardening the servers and hosting environments that everything else runs on: an area with direct, provable experience already (malware remediation, WordPress hardening).
Cloud Security
Assessing and securing cloud-hosted infrastructure across major cloud providers.
Database Security
Protecting the data layer: often the highest-value target in any system.
Penetration Testing
Hands-on, manual, adversarial testing that simulates a real attacker: the highest-credibility service in the portfolio and the one clients most associate with cybersecurity.
Compliance & Governance
Hands-on, manual, adversarial testing that simulates a real attacker: the highest-credibility service in the portfolio and the one clients most associate with cybersecurity."
Security Monitoring & Incident Response
Ongoing services for clients who want continuous protection, not just a point-in-time check.
Zero-Trust Architecture Design
A higher-tier, architecture-level offering for clients with elevated risk profiles or complex access requirements.
Secure Your Web Applications, Protect Your Business
In today's digital world, cyber criminals are constantly finding new ways to exploit web
applications. A single security flaw can cost your entire business — data theft, loss of
customer trust, and major financial damage. At HoffnMazor, we don't just fix vulnerabilities; we
build a complete security shield around your applications.
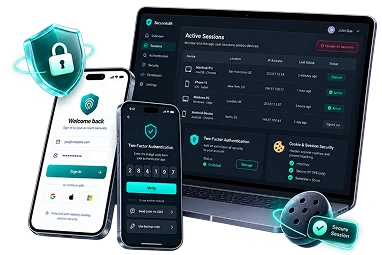
Session & Authentication Security
Review of cookie security flags (HttpOnly, Secure, SameSite), JWT implementation
(algorithm confusion, weak signing secrets, expiration handling), and protection against
session fixation and hijacking.
CSRF Protection
Verifying anti-CSRF tokens and SameSite cookie policies are correctly implemented on all
state-changing requests.
CORS Configuration Review
Identifying overly permissive cross-origin policies that expose APIs or data to
unauthorized domains.
OWASP Top 10 Assessment
Systematic testing for injection flaws (SQLi, command injection), broken authentication, cross-site scripting (XSS), broken access control, security misconfiguration, and insecure deserialization: the vulnerability classes responsible for the vast majority of real-world web breaches.
Security Headers & CSP
Implementing and auditing Content Security Policy, HSTS, X-Frame-Options, and related headers to reduce attack surface at the browser level.
TLS/SSL Configuration
Certificate validity, cipher strength, and protocol version review to eliminate downgrade and man-in-the-middle risk.
Mobile Application Security
Protect What Your Users Trust
Securing iOS and Android applications against device-level and network-level threats. Mobile apps
handle sensitive user data every second — making them a prime target for hackers.
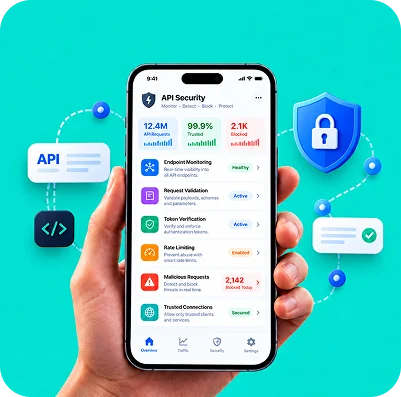
API Security Protecting Every Connection, Every Request
APIs are the connective tissue of modern applications: and one of the most commonly
under-tested attack surfaces. HoffnMazor secures your APIs against unauthorized access, data
breaches, injection attacks, and abuse. From authentication testing to rate limiting and
encryption, we make sure every API call is safe, verified, and protected.
Secure Apps Build Trusted Brands !
Insecure Data Storage Review:
Checking for sensitive data (tokens, credentials, PII) stored unencrypted in local
storage, shared preferences, or plist files.
Certificate Pinning:
Implementing and verifying SSL pinning to prevent traffic interception via proxy
tools.
Reverse Engineering Resistance:
Code obfuscation and tamper-detection review to raise the cost of decompiling and
analyzing the app binary.
OWASP Mobile Top 10 Assessment:
Structured testing against the mobile-specific equivalent of the web OWASP list
(improper platform usage, insecure communication, insufficient cryptography).
API Communication Security:
Verifying mobile-to-backend traffic is authenticated, encrypted, and resistant to
replay attacks.
Broken Object-Level Authorization (BOLA) Testing
Verifying users cannot access or modify data belonging to other users by manipulating
object IDs in requests.
Authentication & Authorization Flow Review
Testing OAuth2/OIDC implementations, token scoping, and privilege escalation paths.
Input Validation & Injection Testing
Ensuring all API inputs are validated server-side, not just at the client.
Rate Limiting & Abuse Prevention
Testing for missing or bypassable rate limits that allow scraping, brute force, or
resource exhaustion.
Infrastructure Security Defense at Every Layer
Your IT infrastructure is the backbone of your entire business — and a single weak point can
bring everything down. HoffnMazor secures your servers, networks, endpoints, and systems against
cyber attacks, unauthorized access, and internal threats.
Locking down shared hosting environments, reviewing account isolation, and auditing for
common misconfigurations.
Firewall & Network Segmentation
Configuring firewalls and security groups to restrict traffic to only what's necessary.
SSH Hardening
Enforcing key-based authentication, disabling root login, and deploying brute-force
protection.
Web Server Configuration Review
Hardening web server software and configuring WAF rules.
Log Monitoring & Alerting
Centralized logging and anomaly detection to catch compromise attempts early.
Databases are the highest-value target in any system, and protecting the data layer
is critical to your overall security. At HoffnMazor, we enforce least-privilege database
users
and roles through Access Control Review, eliminating shared or overly permissive
credentials. We
implement Encryption at Rest & in Transit, using transparent data encryption and encrypted
connections to keep your sensitive information safe. Our team also verifies SQL Injection
Prevention by ensuring parameterized queries and safe ORM usage across your application.
We go beyond traditional databases with a NoSQL-Specific Risk Review, testing for NoSQL
injection and insecure default configurations — a gap many teams miss, since NoSQL injection
is less commonly tested than SQL. Backup Security is another focus area, ensuring your
backups are encrypted and access-controlled, not left as an overlooked exposure point.
Finally, our Database Auditing services include query logging and anomaly detection to
identify unusual access patterns before they become breaches.
250+
PROJECTS DELIVERED
98%
CLIENT SatisFraction
40%
INCREASED PRODUCTIVITY
24/7
SUPPORT & MAINTENANCE
Web Application Penetration Testing
Manual exploitation attempts against the OWASP Top 10 and business-logic flaws that
automated scanners miss.
API Penetration Testing
Manual testing of authentication bypass, authorization flaws (BOLA), and rate-limit
evasion.
Network Penetration Testing
Port scanning, service enumeration, and vulnerability exploitation across exposed network
infrastructure.
Cloud Security for AWS, Azure & GCP
The cloud powers modern business — but without proper security, it can also become your biggest
vulnerability. HoffnMazor secures your cloud infrastructure across AWS, Azure, and Google Cloud
with misconfiguration detection, access management, data encryption, and continuous monitoring.
We ensure your cloud environment is safe, compliant, and always under control.
Checking function-level permissions and event-source validation to prevent injection via
cloud triggers.
Encryption Review
Verifying data is encrypted at rest and in transit, with proper key management practices.
Cloud Logging & Monitoring
Ensuring cloud-native logging is enabled and reviewed for suspicious activity.
Dig Our Appland for Every Niche
Explore our Appland. From gaming to productivity, we've got an app for everything.
Laravel
AWS
Express.js
Node.js
Vue.js
MongoDB
React.js
Django
.NET Core
Docker
TypeScript
Python
PostgreSQL
MySQL
Node.js
GitHub
Book A Free Call!
Curious Cat?
Got a long list of question? We got all the answers. Ask away, and we'll clear the air.
- Samuel K
Product Manager, TechNova
They nailed it. I had a rough idea, and they turned it into something way better than I imagined. Smooth process, great team!
– Jordan T
COO, SwiftTech
Couldn’t be happier with the app! It’s exactly what we needed and works perfectly. They were on point every step of the way.
– Lisa M
Founder & CEO, FitBoost
This team gets it. From start to finish, they made everything easy. My app looks amazing and runs even better!
- Claire R
Chief Technology Officer, UrbanVoyage
I was blown away by their attention to detail. They took the time to understand my vision and brought it to life with zero shortcuts.
- Mariah D
Head of Product Development, TaskMaster
If you’re looking for a team that really listens and delivers, look no further. They created something truly unique for us.
-Kevin S
Chief Executive Officer, DigiSolutions
The whole experience was seamless. They kept me updated, met every deadline, and the final product speaks for itself. Highly recommend!
– Lisa M
Founder & CEO, FitBoost
Great people to work with, seriously! They made the whole thing easy to understand and helped bring my idea to life without a hitch.
- Claire R
Chief Technology Officer, UrbanVoyage
I had high expectations, and they delivered. The app not only looks great but functions better than I hoped. Couldn’t ask for more.
frequently asked questions
Cyber security protects your systems, applications, networks, and sensitive data from cyber threats, unauthorized access, malware, and other security risks.
Hoffnmazor provides security solutions designed to identify vulnerabilities, strengthen your digital infrastructure, detect potential threats, and reduce the risk of security breaches.
We help businesses address risks such as malware, phishing, ransomware, unauthorized access, data breaches, web application vulnerabilities, and other evolving cyber threats.
Yes. We assess web applications for security vulnerabilities and help strengthen them against common attacks, unauthorized access, data exposure, and other application-level risks.
Security testing should be performed regularly, especially after major application updates, infrastructure changes, or the introduction of new systems. Regular assessments help identify emerging vulnerabilities before they become serious threats.
Yes. A strong cyber security strategy helps protect confidential business information, customer data, credentials, and other sensitive assets through security controls, monitoring, vulnerability assessment, and proactive risk management.
 Protect What Your Users Trust








They nailed it. I had a rough idea, and they turned it into something way better than I imagined. Smooth process, great team!